Security Verification and Offensive-Defensive Practice
Why do the "vulnerability researchers" and "operators" always fail to see eye to eye?

Security departments usually have two core main forces: one is the vulnerability management team, and the other is the security operations (SOC) team.
These two teams fight for the company's security every day and work extremely hard. However, if we carefully observe their daily work, we will find a very strange phenomenon: it seems as if they live in two parallel worlds.
First, let's look at the "vulnerability" world. Their work revolves around vulnerability scanning tools, CVE databases, and ticketing systems. Their language consists of CVSS scores, technical details, and remediation plans. Their KPIs are usually "high-risk vulnerability remediation rate" and "service-level agreement (SLA) for vulnerability closure." They spend every day pushing IT and business departments to apply patches, playing the role of "quality inspectors."
Now let's look at the "operations" world. Their main battlegrounds are SIEM, EDR, and SOAR. Their language consists of alerts, logs, IOCs, and ATT&CK. Their KPIs are "mean time to detect (MTTD)" and "mean time to respond (MTTR)." They chase real attack events every day, acting like alert patrol officers.
Here comes the question: What is the connection between the thousands of vulnerabilities found by the quality inspectors and the attackers caught in the real world by the patrol officers?
In many companies, this connection may be much smaller than we think.
Management blind spots are wasting half of our energy
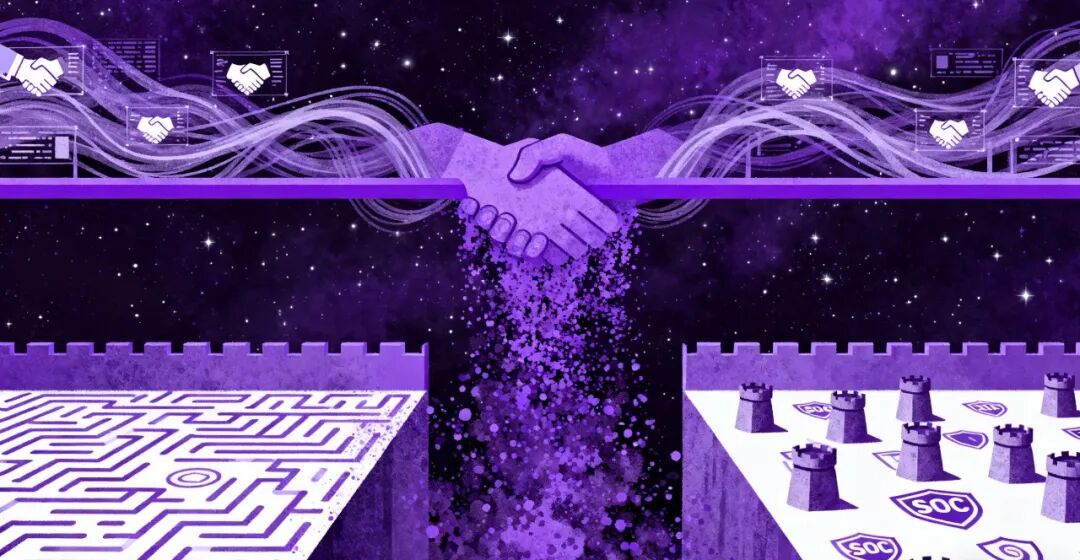
This disconnect is causing a huge waste of resources and management blind spots.
The "vulnerability team" is dispatching tickets blindly. When they see a vulnerability with a CVSS score of 9.8, they immediately set it as the highest priority, requiring the business department to fix it within 24 hours, even at the cost of disrupting operations. But in reality, they do not know whether this vulnerability is truly exploitable in the company's production environment, or if attackers are genuinely interested in it.
The "operations team" is passively putting out fires. They discover a real attack, and only after conducting a post-mortem review do they see that the attacker cleverly chained together three "medium-low risk" vulnerabilities to bypass all defenses. However, because those three vulnerabilities had low scores, they might have been ranked hundreds of places down on the remediation priority list of the "vulnerability team."
The result is: we spend a huge amount of effort fixing dead ends that attackers would never take, while the wide-open avenues that attackers actually successfully exploit are neglected for a long time due to low scores.
These two groups of people are effectively speaking past each other, both working hard in their own ways, but their efforts do not create synergy.
Bridging two worlds requires a common language
To solve this problem, we must find a common language that allows these two teams to communicate. This language cannot be CVSS scores or the ATT&CK matrix, but must be something more direct and indisputable—proven, real-world risks.
This translation work must be completed by an objective validation phase that is independent of both parties.
One of the core values of the SecXOps Security Validation Platform is to act as this translator and bridge. What we do is actually very simple: we take the theoretical risks discovered by the "vulnerability team" and simulate them in a real environment to see if the "operations team" can detect the attack behaviors targeting those vulnerabilities.
Specifically, the process works like this:
Input: Whether it is a CVE found by scanning or a newly exploded 0-day, both can serve as the starting point for validation.
Validation process: The SecXOps Security Validation Platform uses automated attack playbooks to safely and realistically simulate the exploitation of this vulnerability. It does not just test this single point; more importantly, if the exploitation succeeds, it will attempt to continue with a series of actions such as lateral movement and privilege escalation to see how far it can go.
Output: After the validation is completed, the platform outputs two sets of results simultaneously for both teams to review:
For the "vulnerability team": The 9.8-score vulnerability you found was validated, and because there is a WAF in front of it, the attack exploiting this vulnerability was blocked, resulting in an unsuccessful exploit. However, the 6.5-score vulnerability can directly gain control of a Web server and subsequently access the internal network database. If the area where this Web server resides is highly critical—combined with the internal severity level defined by the enterprise for the application and network zone—please raise the remediation priority of the latter to the highest.
For the "operations team": We just simulated an attack on that 6.5-score vulnerability. Your EDR sent an audit log in the 3rd minute, SIEM correlated it only in the 15th minute, and the next-generation firewall's IPS module had no response throughout the process. This indicates that there are two issues, XX and XX, in your detection and response workflows. Please optimize them immediately.
As you can see, through such a validation phase, the work of the two teams is tightly connected. They begin to focus on the same goal: blocking those truly lethal attack paths that have been proven to be effective.
One of the core responsibilities of a security leader is to ensure effective collaboration across the entire security organization. If you find that your vulnerability team and operations team rarely discuss in the same meeting for the same goal, that may be a dangerous signal.
It is time for us to break down the wall between these two parallel worlds.
Incorporate a continuous, automated validation phase into the workflow, using it to align our risk perception and calibrate our work priorities. Let the "vulnerability team" know what to fix first, and let the "operations team" know where to look.
When the two main forces begin to pull in the same direction, the efficiency and effectiveness of the entire security system will experience a qualitative leap.


