Threat Intelligence and Security Incidents
New variant of BiBi Wiper is destroying disk partition tables

A new version of the BiBi Wiper malware variant is deleting disk partition tables, making data recovery much more difficult, thereby extending the downtime of targeted victims.
The BiBi Wiper attacks on Israel and Albania have been linked to a suspected Iranian hacktivist group known as "Void Manticore" (Storm-842), which is believed to have ties to the Iranian Ministry of Intelligence and Security (MOIS).
First discovered in October 2023, BiBi Wiper's activities prompted the Israeli CERT to issue an alert in November 2023 warning of a massive offensive cyber operation utilizing the virus against vital organizations in the country.
The latest report reveals newer variants of BiBi Wiper as well as two other custom wipers used by the same threat group, namely Cl Wiper and Partition Wiper.
Furthermore, there is an operational overlap between Void Manticore and another Iranian threat group, "Scarred Manticore," indicating potential cooperation between the two.
▌False Identities and Cooperative Attacks
Void Manticore is suspected of being the mastermind behind the "Karma" hacktivist group on Telegram, which emerged following the Hamas attacks on Israel in October.
Karma claimed attacks on more than 40 Israeli organizations, publishing stolen data or evidence of wiped drives on Telegram to amplify the damage caused by its operations.
The persona used in the attacks against Albania was named "Homeland Justice", which leaked some of the stolen Telegram files.
This strategy closely mirrors the approach taken by Sandworm (APT44), which is believed to be the power behind hacktivism-branded Telegram channels like XakNet Team, CyberArmyofRussia_Reborn, and Solntsepek.
Another interesting finding is that, in some cases, Void Manticore appears to have handed over control of compromised infrastructure to Scarred Manticore.
Scarred Manticore focuses on establishing initial access, mainly exploiting the Microsoft Sharepoint CVE-2019-0604 vulnerability, performing SMB lateral movement, and collecting emails.
Subsequently, the compromised organizations are handed over to Void Manticore, which is responsible for executing the payload injection phase, network lateral movement, and the deployment of data wipers.
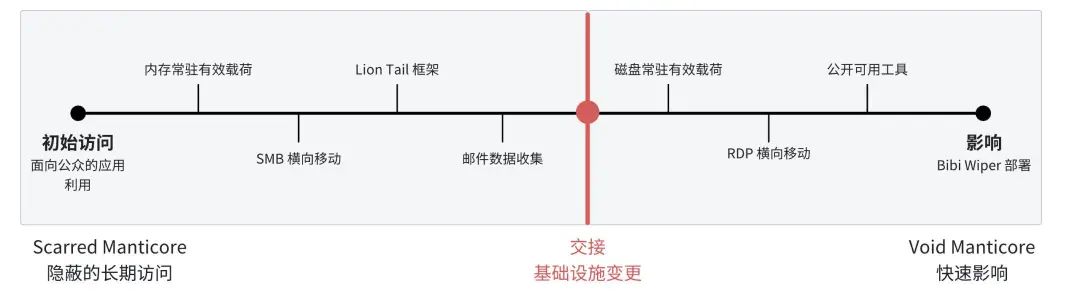
Cooperation between Scarred and Void Manticore
▌Void Manticore Tools
Void Manticore uses a variety of tools to perform destructive operations, including web shells, manual deletion tools, custom wipers, and credential validation tools.
Karma Shell, the first payload deployed on compromised web servers, is a custom web shell disguised as an error page that can list directories, create processes, upload files, and manage services.
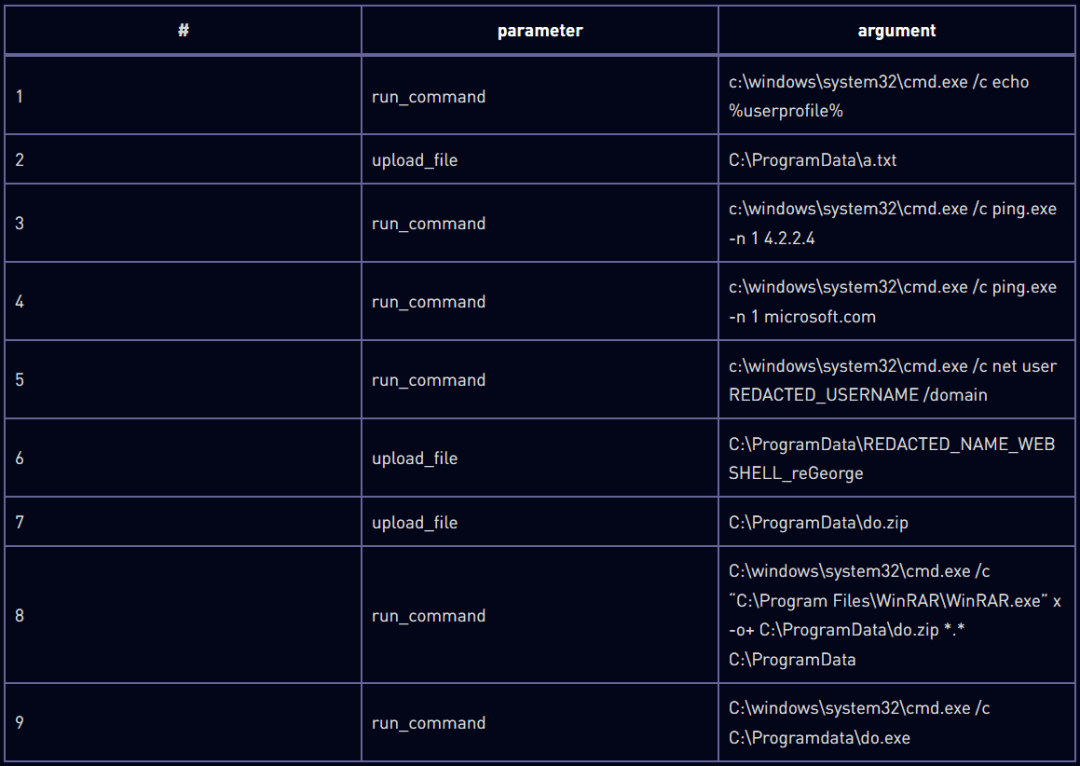
Commands executed via Karma Shell
Check Point discovered that newer versions of BiBi Wiper corrupt non-system files with random data and append randomly generated extensions containing the string "BiBi".
BiBi exists in both Linux and Windows versions, with each version retaining some unique features and minor operational differences.
For example, on Linux, BiBi will spawn multiple threads based on the number of available CPU cores to speed up the wiping process. On Windows, BiBi will skip .sys, .exe, and .dll files to avoid rendering the system unbootable.
Compared to previous versions of the malware, the new variants specifically target Israeli systems and do not delete shadow copies or disable the system's error recovery screen. However, they now delete partition information from the disk, making data recovery much more difficult.
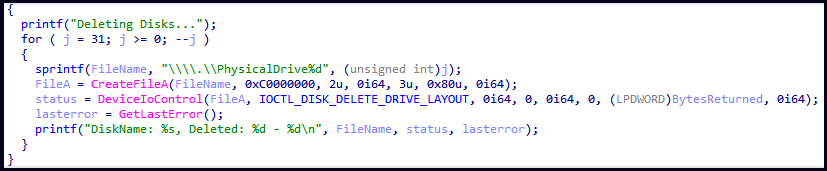
Partition wiping code in BiBi and Partition Wipers
First appearing in attacks against Albanian systems, CI Wiper employs the "ElRawDisk" driver to perform wiping operations, overwriting the contents of physical drives with a predefined buffer.
The partition wiper specifically targets the system's partition tables so that the disk layout cannot be restored, thereby complicating data recovery efforts and maximizing damage.
Attacks by these wipers typically result in victims experiencing a Blue Screen of Death (BSOD) or a system crash upon reboot, as they affect the Master Boot Record (MBR) and GUID Partition Table (GPT) partitions.
Hard drive wipers are extremely dangerous. Once threat groups succeed, it becomes incredibly difficult for enterprises to recover data. Pythesis recommends:
1. Back up your important daily data. Real-time backup is ideal when conditions permit, and regularly practice data recovery to ensure data can be restored if issues arise.
2. You can search for the keyword "Wiper" in the Pythesis Security Metric Validation Platform to obtain all attack simulation validation actions related to hard drive wipers. This will verify whether your security defense system can effectively counter attacks from such malware. The platform ensures your validation process is safe and harmless in an industry-unique way.


