Security Verification and Offensive-Defensive Practice
Oracle has just released the Log4j patch, but security validation must continue!

On April 19, 2022, Oracle released the April patch update advisory. This release contains 520 security patches covering vulnerabilities in Oracle and third-party components. Among them, critical-severity patches accounted for 14.7% of the total, high-risk patches accounted for 27.1%, and medium-severity patches accounted for 55.2%.
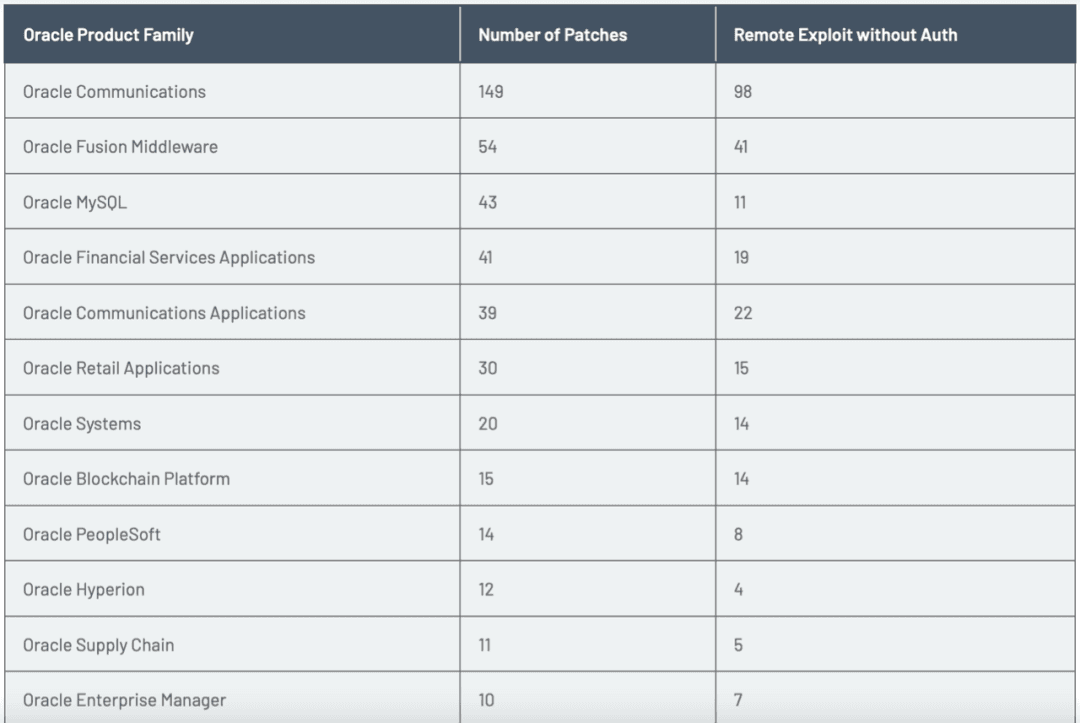
This quarter's patch classification (partial)
▌Highest severity vulnerability — CVSS score 10.0
The patch update released this time includes fixes for 221 CVE vulnerabilities, which also includes two highest-severity vulnerabilities with CVSS scores as high as 10.0: CVE-2022-21431 and CVE-2022-22947.
▌Apache Log4j patches
Among the third-party patches released this time are vulnerability fixes in Apache Log4j.

The original vulnerability Log4Shell (CVE-2021-44228) against Log4j is claimed to be the most serious nuclear-grade vulnerability in the past decade. Attackers' large-scale exploitation of the original Log4Shell vulnerability began around December 9. Security practitioners at Cybeex Security Labs released the latest attack validation library on the morning of December 10, 2021, to allow users to quickly validate it.
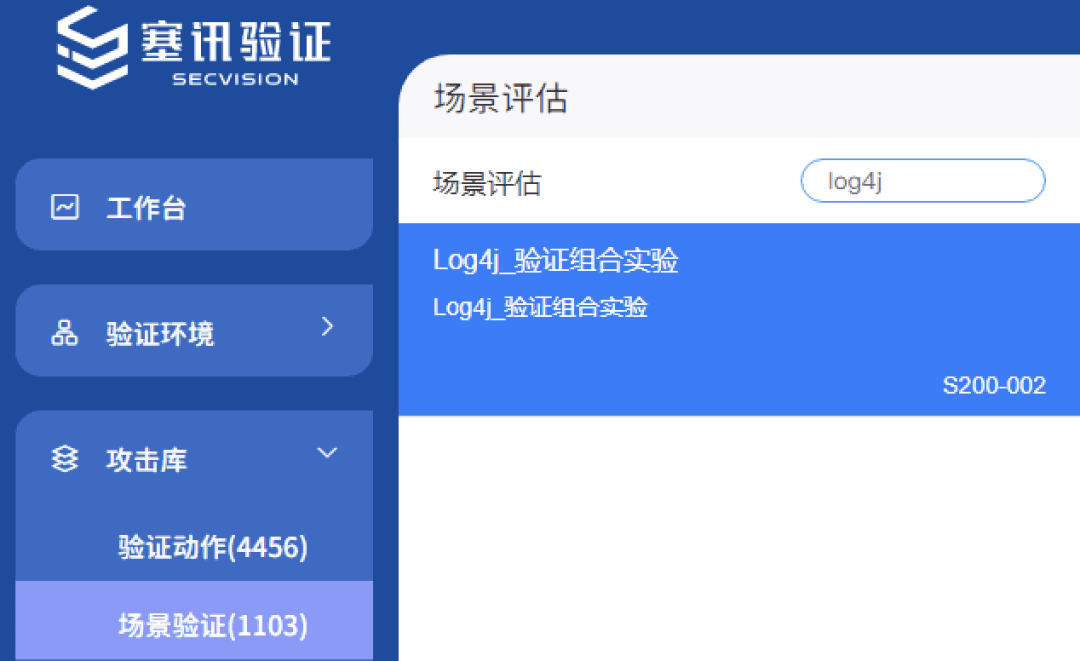
For Cybeex validation users, if you have not had time to upgrade these latest patches to block this vulnerability for various reasons, validating the security defense measures in your environment through the security validation platform is even more important and must be carried out continuously to ensure that no external attacks can successfully intrude by exploiting this vulnerability. Now you only need to search for "Log4j" in the "Scenario Validation" on the Cybeex validation platform to select this validation scenario (as shown in the figure):
The figure below shows the execution results of Cybeex validation customers validating their security defense equipment in production environments:
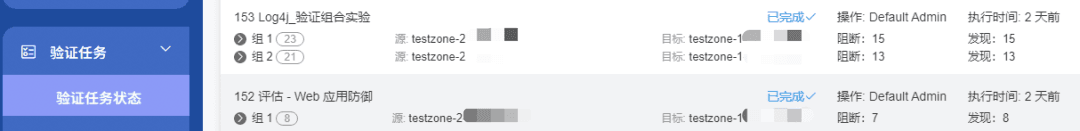
Cybeex validation helps customers timely validate which Log4j-based attacks the security defense equipment takes effect against (blocking or detecting), and provides detailed logs matching this attack automatically obtained after interfacing with the security defense equipment; and which attacks did not take effect (blocking or detecting) as shown below:

When the security defense equipment does not respond, the Cybeex validation platform will send an alarm to the relevant personnel. The relevant personnel can check the configuration of the relevant security defense equipment according to the alarm information. It was confirmed that the failure to detect the attack behavior in this communication was because the security defense equipment did not enable HTTPS decryption.
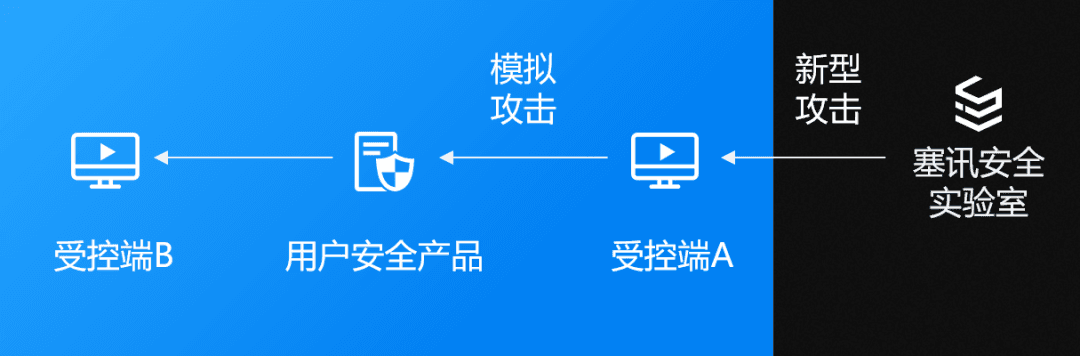
Various security vendors generally launch corresponding protection signature (virtual patch) updates to help users defend against new types of attacks. For users, after updating virtual patches, they cannot quickly validate the effectiveness of virtual patches in the face of real attacks. Cybeex validation can release new attack validation libraries in a timely manner to help users quickly validate them. When the official patch of the vulnerability is released, many users cannot patch it immediately for various reasons. Therefore, Cybeex validation can help users continuously validate the defensive effect of security defense measures, give attackers no opportunity to exploit this vulnerability, and ensure the safe operation of business applications.
| Reference source:
https://www.oracle.com/security-alerts/cpuapr2022.html


