Threat Intelligence and Security Incidents
The Resurgence of LockBit: Escalating Threat or Empty Bluff?

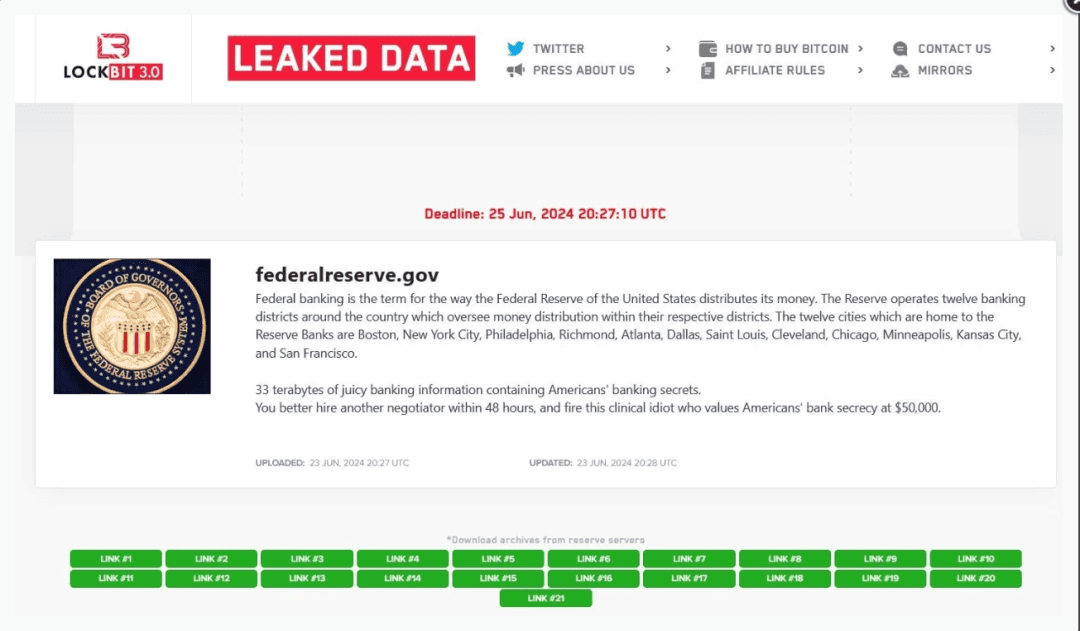
▌LockBit Ransomware Gang Announces Major Breakthrough: 33TB of Sensitive US Federal Reserve Data Stolen
The LockBit ransomware gang recently released a bombshell statement claiming they have successfully breached the US Federal Reserve System and stolen up to 33TB of sensitive data, involving "banking secrets of Americans". The gang quickly went public with their "victory", listing the Federal Reserve on their victim list on their Tor data leak site and issuing a stern warning that they will publish the stolen data on June 25, 2024, at exactly 20:27:10 UTC.
To date, the LockBit gang has not released any samples of the stolen data to prove the authenticity of their claims. However, they detailed the concept of the "Federal Bank" in their announcement, explaining how the US Federal Reserve System distributes funds nationwide through its twelve banking districts, which are located in major cities.
▌Cybersecurity Challenges Amidst the Digital Wave: LockBit Ransomware in the Spotlight
The latest tracking by SecFY Safety Lab revealed that the LockBit ransomware gang's attack activities increased significantly during May 2024, once again proving its activeness and threat level in the current cybersecurity landscape.
The operations of the LockBit ransomware gang suffered a major blow in February this year. At that time, a joint operation by law enforcement agencies in North America, Europe, and Asia seized 34 servers, took over the gang's Tor-based leak site, and successfully froze their cryptocurrency wallets. In addition, law enforcement agencies collected detailed technical information on the gang's infrastructure, providing strong support for future prevention and crackdown efforts.
To encourage the provision of more information, the US government announced a high reward of $10 million for information leading to the leadership of LockBit. Shortly after, multiple individuals associated with the LockBit gang, including Dimitry Yuryevich Khoroshev, suspected of being the mastermind behind LockBit, were indicted. Meanwhile, law enforcement successfully extracted over 7,000 LockBit decryption keys, which undoubtedly dealt a significant blow to the LockBit gang.
▌LockBit Stirs Up Trouble Again: Ransomware Attacks Surge, Severe Global Cybersecurity Situation
In response to the joint crackdown by multiple governments, the operators of LockBit were not to be outdone and launched a new leak site in late February, claiming they were able to restore parts of the disrupted infrastructure. Although their attack speed was slower than before, they continued to launch attacks against organizations worldwide.
By May, the number of global ransomware attacks showed a significant upward trend, increasing by 32% compared to the previous month, and by 8% compared to the same period last year. The LockBit gang was clearly the most high-profile ransomware gang again during this period. They launched as many as 176 attacks, accounting for 37% of all ransomware incidents, with a 665% surge in attack volume.
In contrast, the Play gang ranked second in activity with 32 ransomware attacks launched. RansomHub followed closely in third place with 22 attacks. This series of data once again highlights the ongoing severity of the cybersecurity situation.
▌Proactive Defense: Key Strategies for Enterprises to Fight Back Against Ransomware
In the field of cybersecurity, even as major corporations constantly strengthen their cyber defense capabilities, the most robust security systems cannot guarantee 100% protection against cunning and versatile ransomware gangs. Therefore, enterprises must adopt a proactive defense strategy to seize the initiative in response to escalating cybersecurity challenges. Racing against time and preparing defenses in advance to outrun attackers and other potential target companies, and being the first to perform security effectiveness validation, is the only way to come out on top amidst the omnipresent onslaught of ransomware gangs.
Under the current increasingly severe cybersecurity situation, enterprises need to be more targeted in enhancing their security defense capabilities, specifically reinforcing and improving weak areas and potential threats they face.
SecFY validation users can easily filter and verify whether their security defense systems can effectively withstand the attack techniques of LockBit and other ransomware gangs through its security metrics validation platform. The platform ensures the safety of the validation process in an industry-unique manner, letting you know whether you can stop a real ransomware attack at the last second, without causing any harm to your existing environment.
SecFY maintains a high level of focus on LockBit ransomware, continuously collecting and updating its simulated attack library through its safety lab, with special attention to LockBit-related attack scenarios. Users only need to search for LockBit within the platform to access various LockBit-related variant attack simulation experiments, thereby verifying the effectiveness of their own security defense systems.


