Threat Intelligence and Security Incidents
LockBit 5.0 makes a strong comeback with a fully upgraded ransomware threat

After suffering a heavy blow from the international law enforcement agency's "Operation Cronos" in early 2024, the notorious LockBit ransomware group has staged a comeback. The group's core administrator, LockBitSupp, successfully rebuilt the operational system and recently launched the brand-new LockBit 5.0, internally codenamed "ChuongDong".
This version marks a new stage in LockBit's technical capabilities, with target platforms covering Windows, Linux, and VMware ESXi, and its attack methods are more stealthy and destructive. However, LockBit's road to reconstruction has not been smooth. In May 2025, the group suffered a bizarre security incident—their darknet affiliate panel was hacked, and they were mocked with a message: "Don't do crime, crime is bad, kisses from Prague." This intrusion resulted in the leak of nearly 60,000 Bitcoin addresses and 4,442 negotiation messages, providing valuable clues for law enforcement to track ransom payments. Despite this setback, after LockBitSupp announced a return on a darknet forum, the affiliate system was restarted by requiring new members to pay a deposit of approximately $500 in Bitcoin to obtain the control panel and encryption tools. Security analysis reports point out that LockBit's "Ransomware-as-a-Service" (RaaS) system has fully recovered, and its partner network is active again.
Global organisations face severe threats. Since September 2025, LockBit has launched active attacks again, causing security incidents in more than ten institutions across Europe, the US, and Asia. About half of them used the latest LockBit 5.0, and the rest were still using the older LockBit Black. Statistics show that about 80% of infections occurred in Windows environments, and the remaining 20% targeted virtualisation and server systems. This wave of attacks is not an isolated event. We found that LockBit 5.0 was released in September 2025 to celebrate the sixth anniversary of the LockBit group's establishment, and has now been discovered and deployed in real-world environments. The new version's cross-platform attack capabilities are significantly enhanced, allowing attackers to launch attacks on the entire corporate network simultaneously, with targets ranging from workstations to critical servers hosting databases and virtualisation platforms. The ESXi variant specifically targets VMware virtualisation infrastructure, representing a critical upgrade in LockBit's capabilities. Since ESXi servers typically host multiple virtual machines, attackers only need to execute a single payload to encrypt the entire virtualisation environment, posing a serious threat to enterprises that rely on virtualisation technology. LockBit 5.0 has undergone significant upgrades in encryption speed, obfuscation technology, and detection evasion, and is considered the most dangerous version to date. The new version introduces multi-platform support, providing independent build versions for Windows, Linux, and ESXi, allowing simultaneous attacks on various corporate systems. Its encryption process has been optimised, with improved encryption algorithms to shorten the response time of defenders and achieve rapid full-disk encryption. To evade detection, LockBit 5.0 uses random 16-character strings as the encrypted file extension, effectively bypassing traditional signature detection. In addition, the new version has strengthened anti-analysis functions, making forensics and reverse analysis more difficult by hindering memory dumps and debugging behaviours. The Windows variant of LockBit 5.0 loads its payload via DLL reflective loading and employs anti-analysis techniques, undergoing deep obfuscation and packing. The variant also patches the EtwEventWrite API by overwriting it and inserting a 0xC3 (Return) instruction to disable Windows Event Tracing. Consistent with previous LockBit versions, the new version uses a geographic location check mechanism, terminating execution when a Russian language setting or Russian geographic location is detected, a common practice among Eastern European ransomware groups.
From basic defence to active validation. Facing threats from continuously evolving ransomware groups like LockBit, enterprises not only need to build protective systems but also regularly validate the effectiveness of their security measures. Traditional security protection methods often lag behind the evolution of attack technologies and cannot cope with the rapidly changing threat environment. The SecOps Intelligence Security Validation Platform is already equipped with this ransomware group's latest attack simulation capabilities. By simulating the attack methods of active ransomware families such as LockBit, it can help enterprises regularly validate whether their existing security protection systems can effectively detect and block such threats.
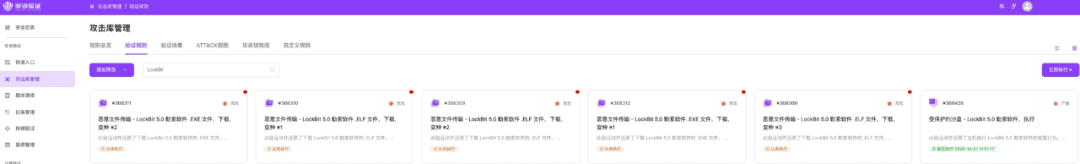
By simulating real attack methods, enterprises can discover protection gaps before suffering actual attacks and adjust their security strategies in a timely manner to ensure they possess real defensive capabilities when ransomware strikes. Only through continuous security validation can they gain the upper hand in this asymmetric cybersecurity war of attack and defence. With the widespread dissemination of LockBit 5.0, enterprises must realise that ransomware threats have entered a new phase. The combination of cross-platform attack capabilities, deep obfuscation technology, and anti-detection mechanisms makes the threat level of this version far exceed that of the past. Only through continuous security validation and protection upgrades can they hold their ground in this asymmetric cybersecurity war.


