Security Verification and Offensive-Defensive Practice
Jaguar Land Rover hit by cross-industry cyberattack: Your security defences must go beyond your own sector

Recently, the severe cyber attack suffered by British automotive giant Jaguar Land Rover caused its production lines to grind to a halt. Jaguar Land Rover's production shutdown has been extended to 1st October, forcing 33,000 employees to take leave. This crisis has not only thrown its ordering system and parts supply into disarray but has also dealt an immeasurable blow to its brand reputation and economic performance. Claiming responsibility for the attack is the notorious hacker group "Scattered Spider", a gang known for high-intensity social engineering attacks and data theft.
The ordeal faced by Jaguar Land Rover is undoubtedly a heavy wake-up call for all enterprises. However, the deeper lesson from this incident extends far beyond alerting the automotive industry. It highlights a harsh reality overlooked by many businesses: threat groups' attack targets are not set in stone, and they can cross industries at any time. Your cybersecurity defenses must never be limited to focusing only on your own sector.
From Aviation to Automotive, Scattered Spider's Industry-Wide Coverage
The attack methodology of the "Scattered Spider" group is highly representative in itself. They do not get bogged down in the complexity of technical vulnerabilities; instead, they excel at exploiting human weaknesses and social engineering, complemented by clever bypasses of MFA (Multi-Factor Authentication) and identity privilege abuse, to ultimately achieve data theft or business disruption. They are like hunters lurking in the dark, patiently searching for the easiest targets to exploit.
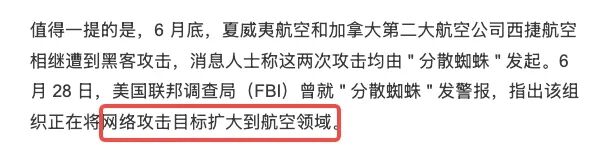
What should alarm us even more is that this group's hunting grounds are expanding rapidly. Just shortly before the Jaguar Land Rover incident, world-renowned Hawaiian Airlines and Canada's second-largest carrier, WestJet, fell victim to "Scattered Spider" one after another. The FBI even issued a dedicated alert for this, clearly pointing out that the group is expanding its attack targets to the aviation sector.
In just a few short months, from aviation to automotive manufacturing — two industries that seem largely unrelated — both have become prey for "Scattered Spider". This clearly illustrates a key characteristic of modern cyber threats: hackers do not necessarily specialise only in specific industries. They focus on the easiest links to breach and the enterprises from which they can extract the greatest value, rather than any specific industry label.
SecurityIllusion is Ready
Against the backdrop of cunning hacker groups like "Scattered Spider" continuously crossing borders to commit cybercrimes, simply focusing on threats within one's own industry is clearly no longer enough. For us at SecurityIllusion, this dynamically changing threat landscape is at the very core of our daily work.
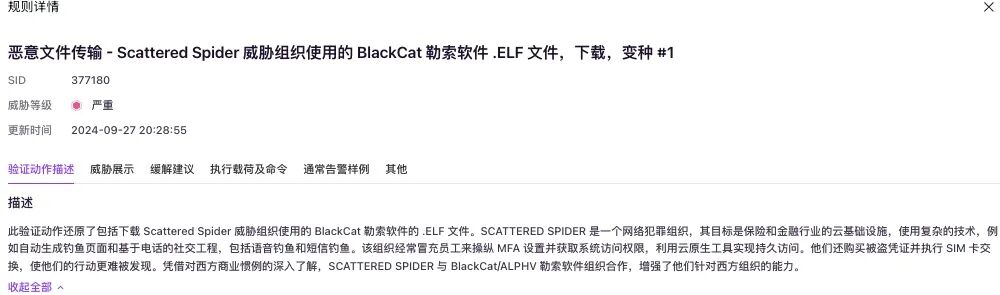
We conducted in-depth research and tracking of "Scattered Spider's" attack patterns very early on. As early as 2024, SecurityIllusion had already incorporated the attack techniques, methodologies, and tactics of "Scattered Spider" into our threat attack library.
We possess a deep understanding and precise simulation capabilities for various attack vectors commonly used by "Scattered Spider", such as social engineering, MFA bypass, and credential abuse.
While "Scattered Spider" is lurking in the dark, trying to find its next target, SecurityIllusion is already capable of translating their attack techniques into actionable defense verification scenarios for enterprises, helping customers discover and resolve potential risks ahead of time.
Is your enterprise only focusing on threats within your own industry?
In the realm of cybersecurity, many enterprises are accustomed to benchmarking against their peers in the same sector. For instance, automotive manufacturers pay close attention to cyber threat reports targeting the automotive industry, while financial institutions closely monitor attack trends in the financial sector. There is inherently nothing wrong with this practice, as industry-specific supply chains, IT architectures, and business processes indeed introduce unique risks.
However, the case of "Scattered Spider" is breaking this defensive mindset of industry barriers. When hackers can easily take attack methods used against airlines, tweak them slightly, and successfully apply them to automotive manufacturers, focusing solely on industry-specific threat intelligence is like watching your own window while ignoring the fire on the roof next door.
The attack capabilities of threat groups and the variability of their targets are far beyond our imagination. Today they target aviation; tomorrow they might move on to healthcare; and the day after, they might aim at critical infrastructure.
This is precisely why security validation requires a comprehensive perspective. As a company dedicated to realistic security validation, truly protecting an enterprise means not being confined to a single industry, specific threat types, or single-point validation.
Dynamic Tracking, Broad Spectrum Coverage: We continuously track the attack methodologies of various threat groups worldwide, whether targeting finance or energy, and include them all in our attack library. For attacks utilizing social engineering and identity management flaws, such as those by "Scattered Spider", they are key research subjects, ensuring we have deep insights into all potential threats.
Simulated Cross-Industry Attack Scenarios: We analyze and abstract common attack techniques and strategies from across different industries' attack activities, translating them into verifiable scenarios. This means that even if your business is in manufacturing, we can test your defense systems using a set of validation scenarios containing attack techniques directed at other industries, preventing cross-industry penetration by hackers.
Predicting Threat Evolution, Early Defense: We do not just track attacks that have already occurred; we focus on the potential movements and evolutionary trends of threat groups. Through comprehensive threat intelligence analysis, we help enterprises identify risks that have not yet broken out in their own industry but could spread at any moment.
Jaguar Land Rover's production halt crisis, along with "Scattered Spider's" consecutive successes in the aviation and automotive sectors, collectively point to a core tenet: cybersecurity defense must break through narrow industry perspectives and address volatile and boundless threats with a broader view. Simply focusing on threats directly related to your own industry is far from enough, as hacker groups' targets and attack methods can be adjusted at any time.
Enterprises cannot afford to wait until they make the headlines to start waking up. SecurityIllusion is ready, integrating the attack capabilities of cutting-edge threats like "Scattered Spider" into our validation services.
By partnering with us to conduct regular, realistic validation covering a wide range of threat scenarios, you can truly prepare for a rainy day. No matter who hacker groups are attacking today, or where they might turn their gaze tomorrow, your business can have the confidence to withstand risks and ensure business continuity because of early, comprehensive preparation.
In this digital era where every industry is a target, let us work together to build an impregnable cybersecurity defense line for your enterprise with a more comprehensive and forward-looking vision.


