Threat Intelligence and Security Incidents
FIN7 Targets Automotive Industry: Utilizing Carbanak Backdoor

Recently, the notorious cybercrime group FIN7 launched a spear-phishing campaign targeting the automotive industry, aimed at delivering the well-known backdoor called Carbanak (also known as Anunak).
FIN7 selectively targets employees in enterprise IT departments because they possess higher administrative privileges. They use free IP scanning tools, commonly used by these IT staff, as bait to run the famous Anunak backdoor and leverage local binaries, scripts, and libraries (LOLBAS) to gain an initial foothold.
FIN7, also known as Carbon Spider, Elbrus, Gold Niagara, ITG14, and Sangria Tempest, is a well-known, financially motivated cybercrime group that has been striking a wide range of industry verticals since 2012, delivering malware capable of stealing information from PoS systems.
In recent years, they have evolved to frequently launch ransomware attacks, as well as deliver various types of ransomware such as Black Basta, Cl0p, DarkSide, and REvil. Two Ukrainian members of the group, Fedir Hladyr and Andrii Kolpakov, have been sentenced to prison in the United States.
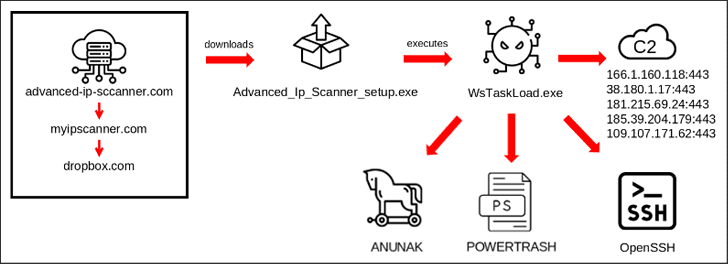
The latest campaign began with a spear-phishing email embedding a phishing link that pointed to a fake website masquerading as an advanced IP scanner ("Advanced – IP – Scanner [.]com").
This fake website redirects to 'myipscanner'. The attackers redirect the malicious executable WsTaskLoad.exe to an attacker-owned Dropbox, downloading it to the victim's machine.
For its part, this binary initiates a multi-stage process that ultimately leads to the execution of Carbanak. It is also designed to deliver additional payloads, such as POWERTRASH, and establish persistence by installing OpenSSH for remote access.
It remains unclear whether the attackers planned to deploy ransomware, as many of the compromised corporate systems were detected early and removed from the network before reaching the lateral movement phase.
Although the preferred target of this attack was a "large multinational automotive manufacturer" headquartered in the United States, several similar malicious domains from the same provider were also discovered, suggesting it may be part of a broader FIN7 campaign.
To mitigate the risks associated with such threats, organisations are advised to closely monitor for phishing attempts, enable multi-factor authentication (MFA), keep all software and systems as well as various security defences up to date, and monitor for unusual login attempts.
Attack simulation rules targeting the tactics employed by this threat group have been integrated into the SecurityGauge platform. You can search for keywords like "FIN7" or "Carbanak" on the SecurityGauge platform to access relevant attack simulation validation actions. This allows you to verify whether your security defence system can effectively counter attacks from this threat group, with the platform ensuring your validation process is safe and harmless in an industry-unique manner.


