Security Verification and Offensive-Defensive Practice
Ditch the Inner Friction, Deliver Real Impact: Unlocking Quality Control Behind Security Verification

In the cybersecurity domain, security validation has become an indispensable part of modern defense systems. The simulated attack library is the cornerstone of security validation products, and the quality of this library determines the upper limit of such products. However, if there is a lack of strict quality control on the attack library, validation products will not only fail to play their due role, but may also increase the time and human costs for users, and even bring security risks caused by misleading information. Therefore, Celsius Security insists on rigorous testing and review of every single security validation rule to ensure its outstanding accuracy and reliability in real-world environments. This quality control system is not only for technical compliance, but also to provide truly effective, detailed information for users' subsequent optimization closed-loop of defense rules, thereby building a more resilient security operations system.
▌In-depth Quality Control: Ensuring the Reliability of High-Quality Validation Rules
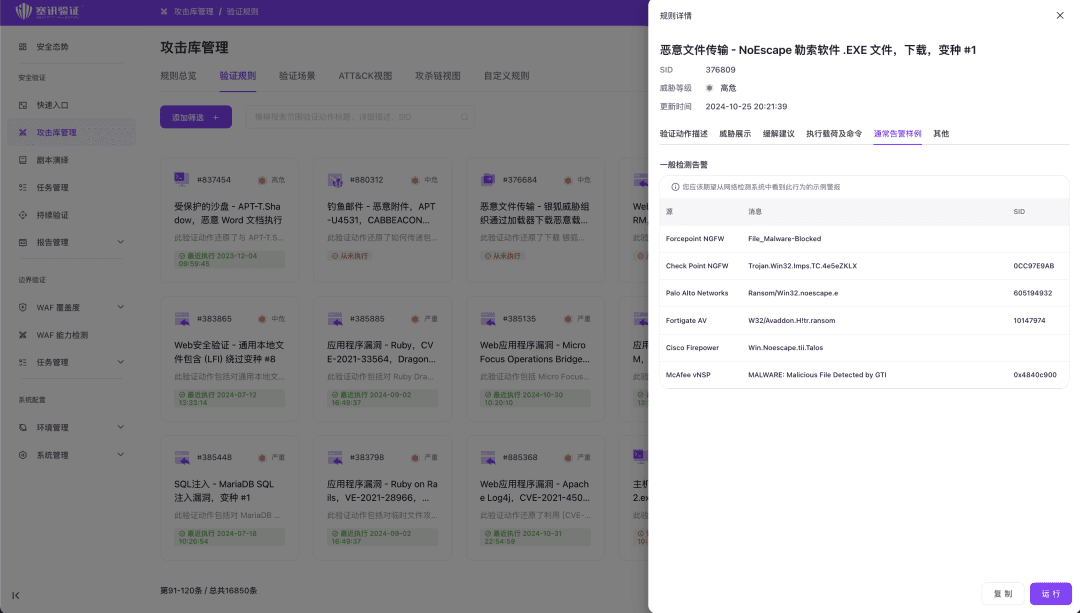
We always believe that high-quality security validation is not only the core requirement of product delivery, but also the foundation of customer trust. Therefore, every validation rule undergoes multi-level testing covering different types of security products before release to ensure stable and accurate operation in various environments. Celsius Security Metric Validation Platform displays tested security product alert information on the page, allowing users to clearly and intuitively see the effectiveness of validation rules, thereby enhancing trust in validation results.
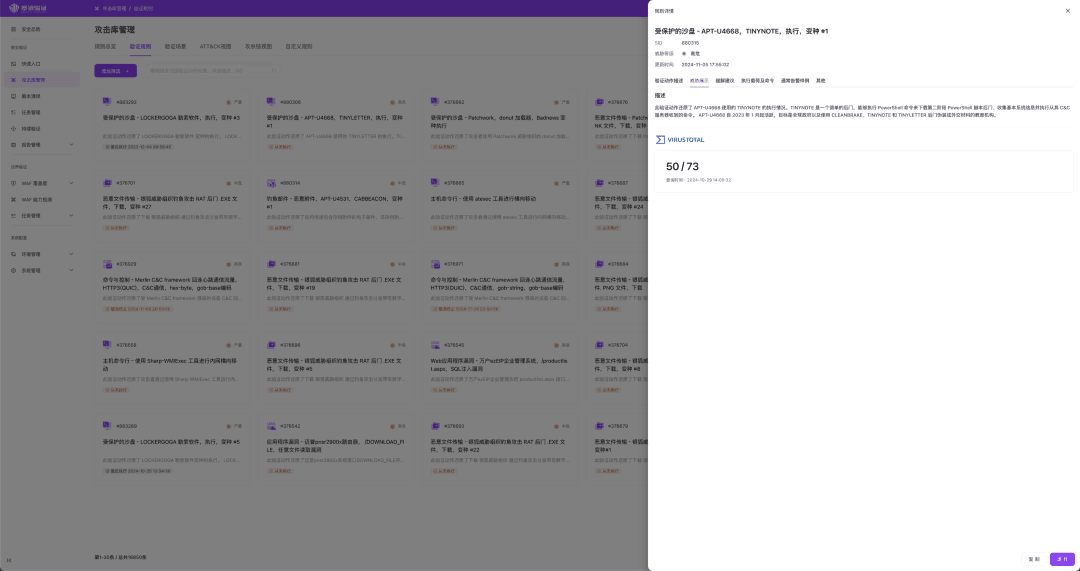
At the same time, the platform also displays query results based on the samples or URLs used in this rule through third-party threat intelligence. This allows users to directly and quickly understand the detection and judgment results of more security vendors worldwide, without having to spend time and effort discussing their authenticity among multiple parties.
During the execution of validation actions, we have set up multiple mechanisms to guarantee the transmission reliability and sequential consistency of data packets, ensuring that there are no error packets or out-of-order packets during transmission, thereby guaranteeing the accuracy and consistency of the execution process. In terms of result determination, the platform primarily judges based on expected outcomes: For example, network-related actions confirm results by receiving expected packet content; terminal-related actions judge by comparing the actual return information with the expected return information; email-related actions validate by receiving expected emails, and so on. The platform not only displays all attack payloads, commands, and sample content, but also provides the expected results of these actions, bringing a transparent validation process to users.

In some special cases, we apply additional processing mechanisms to improve the precision of judgment. For instance, to address minor variations in response content that may occur, we use fuzzy matching to eliminate interference; for multi-command combinations of terminal commands, we introduce comprehensive weight judgment; when dealing with compressed response content, we ensure integrity through decompression and reconstruction.
These precise handling methods enhance the platform's judgment capability in complex business scenarios, providing users with truly reliable security protection.
▌From a Single Product to a Global Perspective: Logical Extension of Security Validation
In modern enterprise cybersecurity architecture, although individual security products have their own advantages, they always have limitations in capability and vision. Therefore, enterprises usually deploy multiple security products to build defense-in-depth. It is essential to organically combine these security products with effective security operations to form a multi-layered, overall defense system. However, to achieve truly effective protection, maximizing individual security product capabilities through security validation alone is still not enough. Under this framework, enterprises increasingly rely on security operations platforms to integrate the capabilities of different security products with other auditing and automated means through correlation analysis and contextual judgment, thereby improving the overall protection level. The core role of security validation has never been limited to the effectiveness of a single security product, nor is it limited to boundary protection. Rather, it simulates a variety of real threat scenarios, including post-exploitation attacks, to validate the collaborative defense effect of multiple security products with security operations platforms and automated response platforms in a full-kill-chain manner. This all relies on attack scenario simulations covering the entire kill chain with contextual correlation. Celsius Security Validation not only focuses on the effectiveness of a single product, but also provides an integrated perspective for security operations, ensuring that various security products work together synergistically.

From a global perspective, a complete kill chain validation must include attack simulations related to the impact and destruction phase. Without this type of attack technique validation, it is difficult to assess the actual response of the defense system facing destructive attacks, yet users often worry that such simulations might cause actual impact on the current environment. To this end, we have constructed an isolated environment where real destructive attacks (such as ransomware) can be executed without overflowing, realizing the simulation of real execution of real samples of destructive attacks. In this environment, we can not only test the protection effectiveness against various destructive attacks, but also observe the defense system's response and recovery capabilities to malicious behaviors, helping users comprehensively improve their cybersecurity protection level from a global perspective. Through this global-perspective validation, Celsius Security Metric Validation Platform can penetrate deep into all levels of the enterprise protection system, enabling enterprises to better evaluate their overall protection capabilities. This multi-layered validation logic helps enterprises identify security shortcomings, optimize protection strategies, and further enhance their security level.
▌Full-Lifecycle Security Validation: Becoming the Backbone of Enterprise Security Construction
In the future, security validation will become an indispensable core capability and tool in security construction, empowering enterprises with continuous and comprehensive security assurance. As cybersecurity requirements continue to deepen, the role of security validation will not just be to validate the effectiveness of a single product or security operations platform, but to further integrate into daily security operations processes, becoming an important cornerstone to ensure the stable operation of the enterprise's overall protection system. First, security validation will penetrate deep into the enterprise's operational processes, and by setting a reasonable validation frequency, regularly check the normal working status of security products, operating processes, work order processing, and log recording, so as to timely discover potential security hazards. Secondly, in policy change management, security validation will automatically validate the configuration and execution of various security policies, including access control, protection policies, and data leakage protection, to ensure that policy configurations are both accurate and effectively executed, avoiding protection vulnerabilities caused by configuration errors or implicit failures. In addition, security validation will gradually connect with various internal platforms of the enterprise to achieve fully automated validation. For example, by integrating with vulnerability scanning platforms, corresponding protection validation can be initiated for specific scanning results, and the blocking effects of key nodes such as accounts, IPs, and sessions can be tested to ensure that protection measures really take effect. Finally, powerful customization features will definitely bring greater flexibility to customers, allowing them to customize the necessary actions required for their unique security operations, and customize the attack techniques they collect that are specific to themselves, so as to achieve all the required validation. In the future, the application scope of security validation will continue to expand, covering account permissions and authentication mechanisms under cloud environments, internal behavior auditing, employee security awareness, as well as the coverage of policies and protective measures. We believe that security validation will become one of the important pillars of the enterprise security system. With the continuous enrichment of validation scenarios, enterprises will gradually form the concept of "validation brings trust", always examining every part of the defense system with a prudent attitude, ensuring that every protective measure can withstand the test of actual threats, thereby creating a truly resilient security protection system.
▌Eliminating Internal Friction, Setting Industry Benchmarks, and Promoting the Standardization of Security Validation
In current security validation processes, users often need to invest extra effort to review and analyze validation results, resulting in increased investment of time and resources without bringing the efficiency gains they deserve. Users' doubts and repeated verifications stem precisely from their lack of trust in the validation results, thus forming what is called "internal friction." As security validation becomes increasingly important in cybersecurity, we see broad prospects for its application in the future: from multi-level protection to comprehensive policy validation, to automated security validation across different platforms, these all paint a beautiful blueprint for enterprises' protection systems. However, to realize these visions, we cannot do without the support of truly reliable and high-quality products. Only a solid product foundation can transform these concepts into practical security protection. Celsius Security Validation always treats every function and technology with a rigorous attitude. We not only focus on industry prospects, but are also committed to perfecting every rule and every validation link to the extreme. We not only provide enterprises with advanced security validation solutions, but also ensure the actual effectiveness of the products in every step of implementation, taking practical actions to drive the industry towards standardization and high quality.


