Threat Intelligence and Security Incidents
BMW hit by data leak as ransomware looms — is your business prepared?

Recently, the global spotlight focused on the BMW Group's encounter with the Everest ransomware group. This notorious group not only claimed to have stolen a massive volume of critical internal documents but also launched a public countdown online, threatening to expose this sensitive data, putting tremendous pressure on BMW.
Everest's extortion methods are typical—not only encrypting data but also stealing it, then leveraging public exposure to exert further pressure, pushing companies into a corner and a double dilemma. They prominently displayed BMW's information on their data leak site, complete with a countdown, clearly attempting to force the company to yield as quickly as possible.
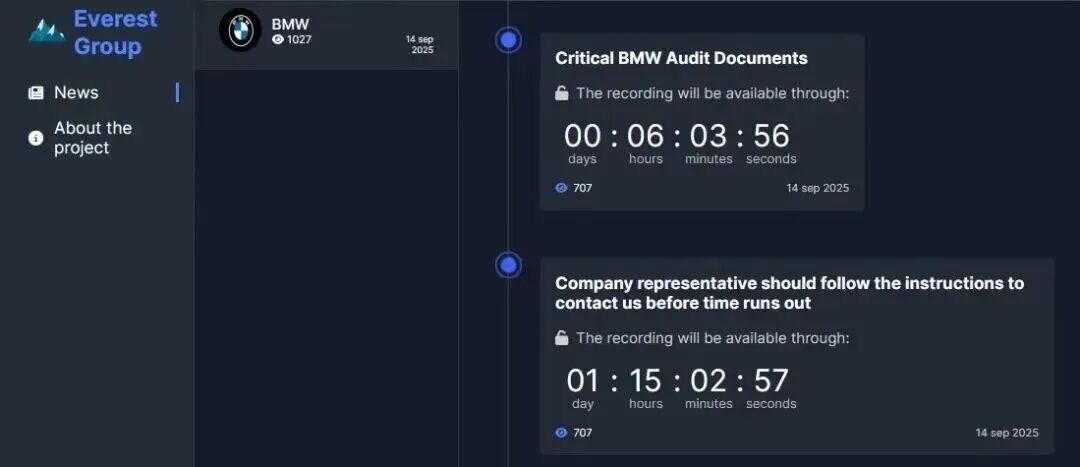
Although the authenticity and specific scope of the stolen documents are still being verified, a volume of 600,000 rows of data is enough to make any enterprise anxious. It could involve core secrets spanning finance, auditing, engineering, and various other aspects, undoubtedly dealing a heavy blow to the company's operations and reputation. This incident serves as another reminder that in the face of cyber threats, no enterprise can sit back and relax. We are no strangers to Everest. The reason the Everest ransomware group is so troublesome lies in their highly sophisticated attack methods and broad targets, regardless of the industry. They do not just encrypt data for ransom; they prefer double extortion—quietly stealing a copy of your sensitive information first, and only then encrypting it. If you don't pay, they release these materials to the public, putting you in a much larger crisis. This strategy leaves enterprises with little room for defense, causing immense pressure. But to SecOps, these tricks from Everest are actually nothing new. As early as last year, our attack library had thoroughly analyzed and catalogled Everest ransomware's various attack paths, behavioral patterns, and the various samples and variants they like to use. We have a detailed understanding of Everest's attack methods, where they might break through, and how they quietly exfiltrate data, and we can simulate them. When the threat of Everest began to emerge, we were already prepared, able to translate these attack techniques into scenarios that enterprises can use to detect and defend in advance.
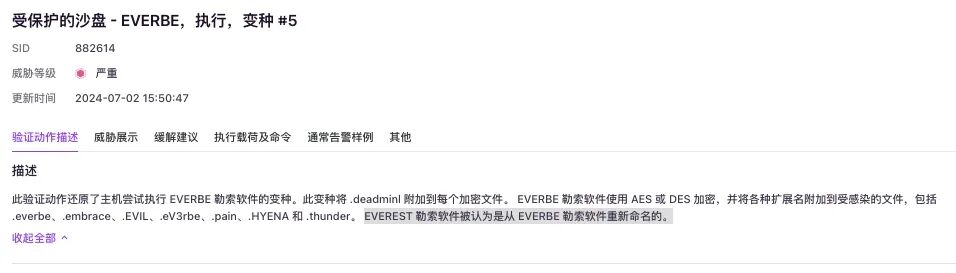
What would happen if validation was performed in advance? Imagine if, before encountering an event like the Everest ransomware attack, an enterprise had worked with SecOps to regularly perform a comprehensive validation of its network security system? The situation would likely be very different. SecOps' approach does not stop at theoretical discussions. We leverage our accumulated library of over 220 ransomware group attacks to realistically simulate, within the scope permitted by the enterprise, various intrusion methods, data theft, and encryption techniques that Everest might use.
Assessment: Simulate vulnerabilities that Everest might exploit to see if your system can withstand these attacks.
Detection: Simulate ransomware spreading within the enterprise's internal network to see if your defense system can detect and block it in time.
Drill: Simulate Everest's process of stealing sensitive files to test whether your data loss prevention measures are in place.
Testing: Attempt to bypass your existing security protection, such as firewalls, antivirus software, EDR, HIDS, etc., to see if they are truly impenetrable.
Through this kind of practical drill, enterprises can discover in advance the potential weak links in their networks, such as patches that haven't been applied in time, misconfigured services, insufficient monitoring in key areas, or signature libraries and policy rules not updated to the latest versions. Once these hidden dangers are identified, SecOps will provide detailed remediation recommendations, advising you on which are the most urgent and need to be prioritized. If we implement all these recommendations, then when Everest actually launches an attack, it will likely find that the intrusion route it wants to take has already been blocked. If it tries to wander around the internal network, it gets caught the moment it moves. Even if it manages to get in, the data it wants to steal is heavily guarded and completely inaccessible; if it wants to encrypt data, it cannot execute it at all. The final result would not be hundreds of thousands of rows of sensitive data being stolen and extorted, but rather a failed attack—a victory where the enterprise successfully defended its lines. This shows that proactive security validation can help enterprises plug those holes that could cause huge losses before danger actually arrives.
Why is security validation a reassurance for enterprises? The BMW incident actually teaches us a truth: security validation is not just to satisfy regulatory requirements, it is a real reassurance that enterprises can give themselves when facing complex and changing threats.
Shifting from passive to proactive: Traditional security measures often wait for an attack to happen before taking remedial action, whereas security validation takes the initiative. It is like conducting a stress test in advance, proactively identifying potential risks so that enterprises can resolve them before they turn into losses.
Real-world effectiveness: Having security policies and theoretical analysis alone is not enough; only by truly simulating attacks can you know whether your defense is actually working. Security validation takes the attacker's perspective, providing real adversarial feedback to help enterprises discover places that look secure but actually have issues.
Stronger through testing: Every validation is an in-depth physical check-up. Not only does it identify problems, but more importantly, it points out the direction for improvement. Through a continuous spiral of validation and improvement, an enterprise's security defense capabilities can continuously upgrade, becoming stronger and consistently maintaining a high level.
Saving money and peace of mind: Once hit by an attack, the losses are not minor: ransoms, legal fines, business downtime, brand damage, customer loss... these all come at a huge cost. Validating and hardening in advance can greatly reduce these risks, ultimately saving the enterprise significant money and countless headaches.
Cybersecurity is not a one-and-done deal. Ransomware attack methods, such as those used by Everest, are upgrading and changing every day. New vulnerabilities are constantly discovered, new variants are constantly created, and new attack methods emerge in an endless stream. Therefore, cybersecurity validation must also be a continuous, dynamically adjusted process, rather than a one-time task. Why persevere? Because attackers are always looking for new breakthroughs. We will continuously track the latest threat intelligence, constantly updating our attack library to ensure our validation scenarios always keep pace with the threats. Moreover, the internal environment of an enterprise is also changing—your IT systems, business applications, and even personnel structures are constantly being updated. New systems going online, old systems retiring, and configuration adjustments can all bring new security risks. Continuous validation can timely detect new vulnerabilities brought about by these changes. Furthermore, security defenses can get fatigued; even the best security products can fail due to misconfiguration, untimely updates, or administrative oversight. Continuous validation is like regularly maintaining your security system to ensure it is always in its best state. SecOps' goal is to provide an end-to-end security validation service to help enterprises maintain the effectiveness and leading edge of their defense systems in a constantly changing threat environment.
The BMW encounter with Everest ransomware once again confirms the fact that cybersecurity risks are ubiquitous, and once they occur, the cost is enormous. If you wait until an attack happens to remedy it, it is often too late. With its constantly updated attack library, keen insight into the latest threats, and realistic validation capabilities, SecOps provides enterprises with a proactive, efficient, and continuously effective security defense strategy. We do not just find problems; more importantly, we provide practical, actionable solutions to help enterprises firmly hold the initiative in the complex and changing cyber battlefield. In this challenging digital age, choosing SecOps is choosing peace of mind for your enterprise—choosing a reliable goalkeeper to jointly build a solid digital defense line, stopping the threat of ransomware at the enterprise's gates.


