Threat Intelligence and Security Incidents
Be alert to global indiscriminate attack threats; Hunters International makes a comeback!

Since the second half of 2023, Hunters International has quietly emerged with its unique Ransomware-as-a-Service (RaaS) model. Its technical techniques are strikingly similar to those of the once-feared Hive ransomware group, quickly attracting widespread attention and vigilance globally. Following the joint crackdown on the Hive organization by multinational law enforcement agencies, the appearance of Hunters International undoubtedly reveals the resilient regenerative capability and extraordinary adaptability of cybercriminal forces.

▌Who is Hunters International?
Hunters International, this cybercriminal group, quietly rose to prominence as Hive fell, becoming a focus of attention. The group first showed its edge in the third quarter of 2023, with a technical architecture identical to Hive's, prompting speculation about whether Hive's "resurrection from the ashes" was hidden behind it. The resilience of the cybercrime world is fully displayed here; even in the face of severe crackdowns, they can quickly adjust their strategies and continue their evil deeds. The rise of Hunters International is undoubtedly a severe test for the global cybersecurity field.
▌Hive Resurrected?
The ransomware techniques and software versions of Hunters International are very similar to Hive's, suggesting they may stem from the same technical source or that a technology transfer took place between the two.
In January 2023, a coalition of multinational agencies, Europol, and other relevant European agencies cracked down on the Hive ransomware gang. Since June 2021, the group had extorted more than 1,500 victims worldwide, involving amounts exceeding $100 million, targeting industries such as healthcare, education, and finance.
In the operation to dismantle the Hive network, the joint agencies gained access to the network through a seven-month undercover operation, providing decryption keys to more than 300 victims and recovering approximately $130 million in ransom. Although no arrests were made, the operation dealt a heavy blow to Hive's operations. Recent investigations suggest that Hive's leadership may have proactively terminated operations and transferred assets to Hunters International.
▌Techniques and Tactics of Hunters International

Security researchers on X (formerly Twitter) stated that the code first released by Hunters International shared about a 60% similarity with Hive's.
In response to these allegations, Hunters International stated that they are not a spin-off of Hive, but rather took over Hive's source code and infrastructure as an independent entity. Their primary operational focus is on stealing data rather than encrypting it, differing from Hive's approach.
Security validation labs have tracked the group's clear preference for data theft, with all victims experiencing data leaks. Hunters International appears to have redesigned Hive's ransomware, reducing command-line options and optimizing encryption key management to make the malware cleaner and easier to operate. They use a unique method to embed the encryption key into the encrypted files, simplifying the decryption process for victims who pay the ransom, further enhancing the impact of the attack.
▌Targeting Strategy
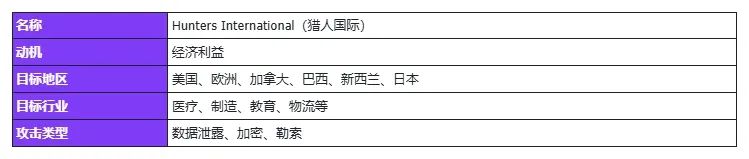
Hunters International's attacks span multiple industries worldwide, with victims including sectors such as healthcare, automotive, manufacturing, logistics, finance, education, and food, indiscriminately targeting all vulnerable entities.
The group is highly active, attacking many different organizations worldwide. Most of their targets are in the United States, but they have also attacked companies and organizations in Europe, Canada, Brazil, and even as far as New Zealand and Japan. They cast a wide net with no specific targets, continuously seeking extortion opportunities and launching operations against targets that may lack robust cyber defenses or urgently need their data, whether they are energy companies, hospitals, schools, or zoos.
This characteristic of indiscriminate attack is common among organizations using the Ransomware-as-a-Service (RaaS) model. The traits of the victim groups highlight the opportunistic nature of the organization and its ability to penetrate various industries, posing a significant threat to all types of organizations globally.
▌Behind the Attacks
As the analysis of Hunters International's attack campaigns deepened, their data leak website gradually surfaced. Through tracking and analyzing domain registration information and email addresses, investigators found a subtle connection between the group and Nigeria. On January 22, 2024, Hunters International launched a non-dark web version of their data leak website, using the same name as the original site.

They repurposed a website that had been unused since 2021, using a pseudonym to mask their true identity, making tracking more difficult. During the investigation, investigators discovered email addresses linked to Nigeria. However, these emails are likely just a tactic used to mislead investigators, making it hard to distinguish truth from falsehood.
Hunters International's ransomware has caused significant data breaches, financial losses, and reputational damage to affected organizations. In response, security validation recommend taking proactive and comprehensive defense measures, including regular data backups, phishing simulations and security awareness training for employees, regular validation of security defense effectiveness, and participating in threat intelligence sharing to enhance resilience against evolving cyber threats.
The emergence of Hunters International reflects the persistence and evolution of cyber threats in the digital age. Despite extensive government efforts to disrupt ransomware, groups like Hunters International still pose a significant risk to global cybersecurity. Continuous validation, proactive defense strategies, and international cooperation within the cybersecurity community will effectively mitigate these threats.
▌Security Validation Rules
In response to this threat group, the security validation platform has added corresponding attack simulation rules. You can search for the keyword "Hunters International" on the platform to obtain attack simulation validation actions related to this threat group. Through these simulated attacks, you can validate whether your security defense system can effectively respond to attacks from this threat group. The security validation platform utilizes an industry-unique method to ensure your validation process is safe and harmless.


