Threat Intelligence and Security Incidents
New FASTCash Malware Linux Variant Attacks ATM Payment Switches

A prominent threat group has been utilizing a Linux version of a malware family named FASTCash to carry out cash-out schemes. This malware is specifically deployed on payment switches within compromised networks, which are responsible for processing bank card transactions. Through this method, attackers can easily and illegally withdraw cash from ATMs. The existence of FASTCash was first documented back in October 2018. However, associated hacker forces have been using this malware since at least late 2016 to execute ATM theft schemes against banking institutions in Africa and Asia.
▌The Attack Evolution and Fraud Techniques of FASTCash Malware
FASTCash fraud rings remotely compromise bank payment switch application servers to execute fraudulent transactions. In 2017, the HIDDEN COBRA criminal group stole cash from ATMs in over 30 countries simultaneously; in 2018, the group again stole cash from ATMs in 23 countries simultaneously. While early FASTCash attacks primarily targeted systems running Windows (with the most recent discovery just last month) and IBM AIX, the latest data shows that a sample targeting Linux systems was first submitted to the VirusTotal platform in mid-June 2023.
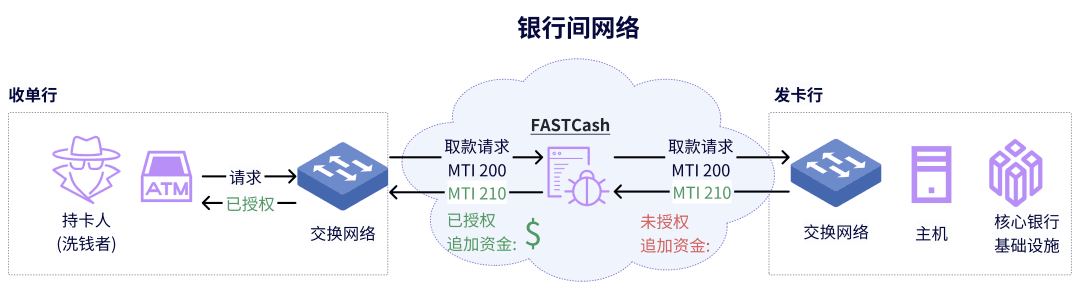
The malware exists as a shared object file ("libMyFc.so") suitable for Ubuntu Linux 20.04. Its design purpose is to intercept and manipulate ISO 8583 transaction messages used for debit and credit card processing, thereby enabling unauthorized cash withdrawals. Specifically, it targets transaction messages that are rejected (via magnetic stripe swipes) due to insufficient funds for a preset list of card numbers, altering and approving these transactions to withdraw random amounts of Turkish Lira.
▌Fraud and Detection Issues of the FASTCash Linux Variant
The amount withdrawn for each fraudulent transaction ranges between 12,000 and 30,000 Turkish Lira (approximately 350 to 875 USD). This fraudulent method is virtually identical to the modus operandi of the Windows version of the FASTCash malware ("switch.dll") exposed in September 2020. Notably, the emergence of this Linux variant has exposed a critical issue, which is that Linux server environments generally lack sufficient detection capabilities. This deficiency could leave the door open for more similar malware, leading to more severe damage in fields such as financial security. Therefore, relevant detection mechanisms urgently need to be improved and refined to enhance resilience against such malicious attacks.
▌Securityworks Validation Rules
In response to this threat group, the Securityworks Security Metric Validation Platform has added corresponding attack simulation rules. You can search for the keywords "FASTCash" or "HIDDEN COBRA" on the platform to obtain attack simulation validation actions related to this threat group. Through these simulated attacks, you can verify whether your security defense system can effectively counter the attacks of this threat group. The Securityworks Security Metric Validation Platform uses an industry-unique approach to ensure that your validation process is safe and harmless.


